
Recruiters are responsible for data collection and processing in a key area that impacts people’s lives. The risk of making mistakes in this area can be high for the company’s reputation and wallet: personal data regulation breaches can result in fines in seven-digit figures.
Therefore, it is important to understand what data to collect, process and store for the recruitment process. With the help of Attorney at Law at Sorainen, Pirkko-Liis Harkmaa, this comprehensive article will provide you explanations and guidelines to ensure GDPR compliance in recruitment.
GDPR (General Data Protection Regulation) is a comprehensive legal framework established in the European Union that provides universal rules for collecting, storing, and using personal data. It applies to automatic and systematic data processing. One of the biggest goals for GDPR is to give EU citizens more control over their personal data. In recruitment, collecting personal data is necessary to make informed hiring decisions, this article will help you ensure you’re doing it in compliance with GDPR.
What is personal data?
Personal data is basically any information relating to a natural person who is identified or can be identified. To be identified or identifiable means that there is an identifier attached to that natural person that directly or indirectly enables the person to be identified, whether by means of single identification data or identifier or, in a combination of those identifiers.
Basically, personal data is everything that is characteristic of a person and that can identify that person to us.
Personal data is not only a person’s name or personal identification number; it could also be location data, online identifiers, or one or more factors specific to the type of physical, psychological, genetic, mental, economic, cultural, or social identity. Personal data also includes the voice, videos, and pictures of that person.
Data processing is any operation or combination of operations performed on personal data or on sets of personal data, whether or not by automated means.

Personal data in the recruitment process
People involved in recruitment have to handle a lot of personal data in the recruitment process. Different types of personal data are collected at various stages, for example:
- Personal information, like name or contact details
- Data about the skills and qualifications (e.g. educational certificates)
- Data about referees and information collected from them
- Data from test results. Including tests for cognitive abilities and personality traits, technical aptitude tests like problem-solving tasks, group exercises, and role plays
- Medical certificates for certain positions
- Medical information when the job requires physical fitness by law
- Data from background checks, criminal records or proof of disability
What is special category data in recruitment?
Certain special category data is usually not allowed to be processed. It’s data that might greatly influence an employee’s or person’s or candidate’s privacy and lead to discrimination or unfair treatment.
Special category data: data revealing racial or ethnic origin, political opinions, religious or philosophical beliefs, or trade union membership, and the processing of genetic data, biometric data for the purpose of uniquely identifying a natural person, data concerning health or data concerning person’s sex life or sexual orientation.
This is the type of data that usually shouldn’t be asked in a recruitment process. In an employment context there are very rare occasions for the need to collect that type of data.
Can I ask about the candidate’s medical conditions during the recruitment process?
The law sets forth very specific positions where prior medical certification is needed. There are very few cases in which prior medical certificates can be requested. For example, for doctors or people who handle food, but in other cases, no prior medical checkups can usually be conducted.
You can ask the employee whether the employee thinks they have any kind of medical condition that prevents him or her from taking up the position. However, the employer should be able to determine whether or not the employee is suitable for the position during the probationary period.
GDPR terms in recruitment
Recording, collecting, retrieving, storing, looking at data, sharing it with someone and erasing it are all data processing operations and qualify the candidates as being subject to GDPR.
We need to understand where to place recruitment-specific terms and parties under the terms used in GDPR.
- The most important person in GDPR is the data subject, who is an identified or identifiable natural person. In the recruitment context, this is our candidate or applicant.
- The other important person is the controller. The controller is the one who alone or jointly with others determines why we need to process the personal data and how we will do it. In the recruitment context, the controller is the employer who identifies what data is needed in order to carry out the recruitment process and find suitable employees.
- The processor is usually the person who is engaged on behalf of the controller to process personal data. In the recruitment context, there are all kinds of third-party service providers, e.g., recruitment service providers and software providers. In the employment context, the processors can be payroll service providers.
The processors can process data only for the same purposes and in the same sets of data as the controller. The processor will not get any wider rights. There always needs to be a written agreement approved with the data processor that outlines what the rights and obligations are.
See how Teamdash keeps candidate data GDPR compliant across teams and countries
GDPR principles in recruitment
GDPR sets out a few principles that apply to every step of recruitment, from the job ad to deleting candidate data when the process ends.
Data processing always has to be lawful, fair and transparent
This means that there must always be an appropriate legal basis that enables us to process the data.
Data processing must be fair. It cannot extensively interfere with the data subjects’ rights to privacy. So, the controller must always weigh its own interests against those of the individuals. This must be done before any processing activities are commenced.
The controller must be open and clear about processing and notify all the data subjects what is being done with their data.
We must always identify a specific, explicit, and legitimate purpose for which we collect the data in the recruitment context.
Purpose limitation
When we have set our goal, i.e. the purpose for which we process the data, processing is allowed only for this specific purpose, and it has to be compatible with the initial goal that we set. In recruitment, we usually collect data to select the best candidate for the job.
If we wish or need to process the collected data for any other purpose that we didn’t identify in the beginning, we are not allowed to do so unless we notify the data subjects.
Data minimisation and accuracy
Data minimisation means that, when we consider the purpose we have set for our data processing, we only process information to the extent that it is strictly necessary to achieve this purpose.
We only need to see what the minimal amount of data is to achieve the purpose that we have initially set for ourselves. Any other data is nice to have, but it shouldn’t be collected.
Minimising data also helps manage it better. Inaccurate data can result in consequences for the data subjects. Therefore, we must always ensure that the data we have collected is and remains accurate. If we have doubts about its accuracy, we need to update it to limit any negative results or harm to data subjects.
Storage limitations
Again, the purpose is everything. When we consider all the other principles, once we have set the purpose, we can store the data collected for that purpose until the purpose is exhausted.
This means that once the successful candidate has been selected, there is no longer a need to retain the candidate’s data. We must then implement proper technical and organisational measures to delete the data and/or keep the data secure (with consent) and protect it against unauthorised or unlawful processing.
The accountability aspect or accountability principle
The accountability principle means that the data controller has the obligation to ensure compliance but should also be able to prove that they have been compliant with the GDPR in their activities. The controllers are accountable for what they are doing with the personal data they collect. This becomes very important when something has happened and we are talking about imposing rather extensive monetary penalties on the controllers.
What data can we collect in recruitment?
Basically, we can collect data which helps to determine the candidate’s suitability for the job offered.
We usually have the purpose of selecting the best candidate for the job.
Therefore, we can collect, or even need to collect, information that helps us determine whether the candidates are suitable or not. We cannot collect data that disproportionately concerns the candidate’s private life or is not related to the suitability assessment for the job offered.
According to the purpose limitation and data minimisation principles, you can only ask for information or data that is necessary and relevant when you consider the purpose of selection of the best candidate.
You should avoid irrelevant details and invasive questions.
Even if the candidate themselves provides all kinds of additional nice-to-have information about themselves, that information should not be processed.
Usually you don’t need to keep it; sometimes, you must even delete it because it’s not relevant to your decision-making process.
Tip: If you don’t need that data to make an informed decision about the candidate, delete it immediately. The more data you have, and the more you think you might need it in the future, the more data you need to provide to the employee or the candidate when they decide to exercise their right to get information.
How to determine the data you need to collect in recruitment?
First think about the job requirements, which are usually found in job profiles, to determine the data you need to collect. These should also be mirrored in the job ads that you publish.
What you include in your job profiles and job ads are not important only in terms of GDPR compliance, but also later on when you need to defend yourself against any claims regarding discrimination or unfair treatment in the recruitment phase or when you have already employed someone. This gives you the basis for assessing whether the person is suitable during the probationary period and also allows you to take measures when under-performance or breach of duties occurs.
Therefore, job profiles and job ads are very important documents. If they are very brief, this can sometimes be a problem later on in the employment relationship as well.
When you have thought through what expectations you have for the candidates and for the job, then this helps you also to determine what kind of data you need to assess the candidate against so that you can find the best one for your job.
Certain data becomes relevant only at later stages, for example, when you have chosen the top three or even the final candidate, you might need their bank account details. This data becomes relevant only in the later stages, not when the candidate enters the recruitment process.
Consent in recruitment
In recruitment, you need consent for processing of special category data, contacting referrals and retaining candidate information for the purpose of future vacancies in your talent pool.
It is very common for people to think that consent is always the right ground or that consent allows me to collect or process anything I want. That is not true.
- One very important element of consent is that it needs to be given freely. If it’s determined that the consent has not been given freely, then it’s void. So it means that the candidate must have a real possibility of not giving the consent without any detriment to results. We cannot bundle the consent with any other kind of expression of will.
- Consent always needs to be separate, very clearly formulated, and in easy-to-understand language. It has to be granular in the sense that we cannot take a blanket consent that would cover, for example, all or three instances where processing is consent-based. The candidate needs to have an opportunity to pick and choose what they consent to.
- Consent has to be very specific and informed, which means that all aspects relating to consent-based data processing have to be made known to the candidate.
- Consent cannot be given in a passive manner. There always has to be some action on the part of the candidate, there cannot be any pre-filled tick boxes. Otherwise, the consent is not GDPR compliant.
- Consent should be transparent. Before deciding to submit their application, the candidates should be aware of what will happen to the personal data they submit as part of the recruitment process. And they should know what kind of data you collect.
One very important aspect of consent is that it does not legitimise any data processing purpose or activity that might otherwise not be justified.
For example, you cannot argue that you processed sensitive data about a candidate’s plans to have children in the next two years, and she agreed to provide such data. This doesn’t make the data processing legal.
Candidate consent for recruitment agencies
If you are a recruitment agency and you want to collect a talent pool and mediate these people to other potential employers, then you are yourself a data controller. In this case you have a different kind of relationship with the people who are in your talent pool.
You need their consent to keep them in the database for future vacancies. But if they apply through you only for a very specific position, then you don’t need their consent to use the data only to assess whether they are suitable for that specific position.
Privacy notice for candidates
There needs to be a privacy notice for candidates.
You can add a link to it in the job ad or provide it in some other manner in the recruitment process. Either way, candidates should be aware of what is going to happen before they submit their data. The privacy notice must comply with certain requirements of the GDPR and needs to be accessible to the candidates, informing them what data you are processing, why you do it, how you do it, on what basis and who processes it.
You also need to inform the candidate who has access to the data, whether you use any data processors, whether you transfer the data abroad, what the candidates’ rights are, and how they can exercise their rights.
One requirement of the privacy notice is that it has to be very easily comprehensible for candidates and in easy language.
Tip: Usually, I would recommend this privacy notice to be a separate one because in most cases, the data sets and the purposes differ from the usual employee data processing or other data processing in the company. I would recommend not trying to combine everything into one document or to make a very long document because then it is not very easy for people to understand.

How long can you store candidate data?
GDPR does not determine the number of months or years for retaining the data. The simple answer is that you can retain the data until it has served its purpose – that is until the successful candidate has been chosen or until the statute of limitation period for claims relating to the recruitment process has expired.
In Estonia, for example, the statute of limitation period for these types of claims is 12 months. So, it’s justified and legitimate to keep the candidate data for 12 months.
You should keep only such data as is necessary to defend yourself against the possible claims that the unsuccessful candidates might bring forward.
If you want to retain candidate data for any future vacancies, then consent is always needed. Otherwise all data needs to be deleted.
Tip: Every time, you need to assess what is the purpose of collecting this data ask the question: has this purpose been exhausted? If you determine that it has been exhausted, you will have to delete the data to be GDPR compliant.
Candidate rights in recruitment
Candidates have several rights, most importantly, everybody has the right to access their personal data.
Candidates have the:
- Right to access data
- Right to data rectification
- Right to be forgotten
- Right to restrict processing
- Right to data portability
- Right to object to processing
- If it’s consent-based processing, then they have the right to withdraw the consent.
There are several other important aspects of the accountability principle. It’s very important to ensure that data is kept confidential and candidate privacy is respected. This also includes the prohibition of disclosing data arbitrarily.
You need to disclose recruitment data only on a need-to-know basis and keep recipients of such data to a minimum. For example, it’s not good practice to share the candidate’s CVs or data with everybody in the company. When you have done so and the candidate asks about their data usage, you have to provide the information about everybody to whom you have sent this data.
Another important thing to keep in mind is that every controller and data processor has to keep a register of processing activities. This can also help you streamline the processes in your company and get rid of unnecessary processing activities or unnecessary data.
GDPR when you hire in several countries
GDPR is the same across the EU and EEA, but hiring in several countries still adds local layers. Candidate data moves between head office, local HR teams, hiring managers and service providers, often in different countries, and every country has its own rules on top of GDPR.
What can differ from country to country:
- Retention periods. GDPR doesn’t set a number of months. Local limitation periods for recruitment-related claims decide how long it’s reasonable to keep unsuccessful candidates’ data. In Estonia it’s 12 months, but other countries differ.
- What you can ask and check. National employment law sets the rules for background checks, criminal records and health checks, and they vary a lot.
- Language. A privacy notice has to be easy for candidates to understand, which in practice means writing it in their language.
- Supervisory authorities. Each country has its own data protection authority, and their guidance on recruitment can differ in detail.
- Transfers outside the EEA. If candidate data goes to a team or provider outside the EU or EEA, you need a valid basis for the transfer, such as an adequacy decision or standard contractual clauses.
How to keep it manageable:
- Set one recruitment privacy policy for the whole group, then add the local details: retention period, contact person and language.
- Publish a candidate privacy notice for each country or brand, and link it in every job ad and application form.
- Agree retention periods per country with your legal team, and automate deletion or anonymisation where you can.
- Give access by team and project, so hiring managers only see candidates for their own roles.
- Keep a list of every tool and provider that handles candidate data, with a data processing agreement for each.
- Check where your tools store data, and what happens to data sent to AI features.
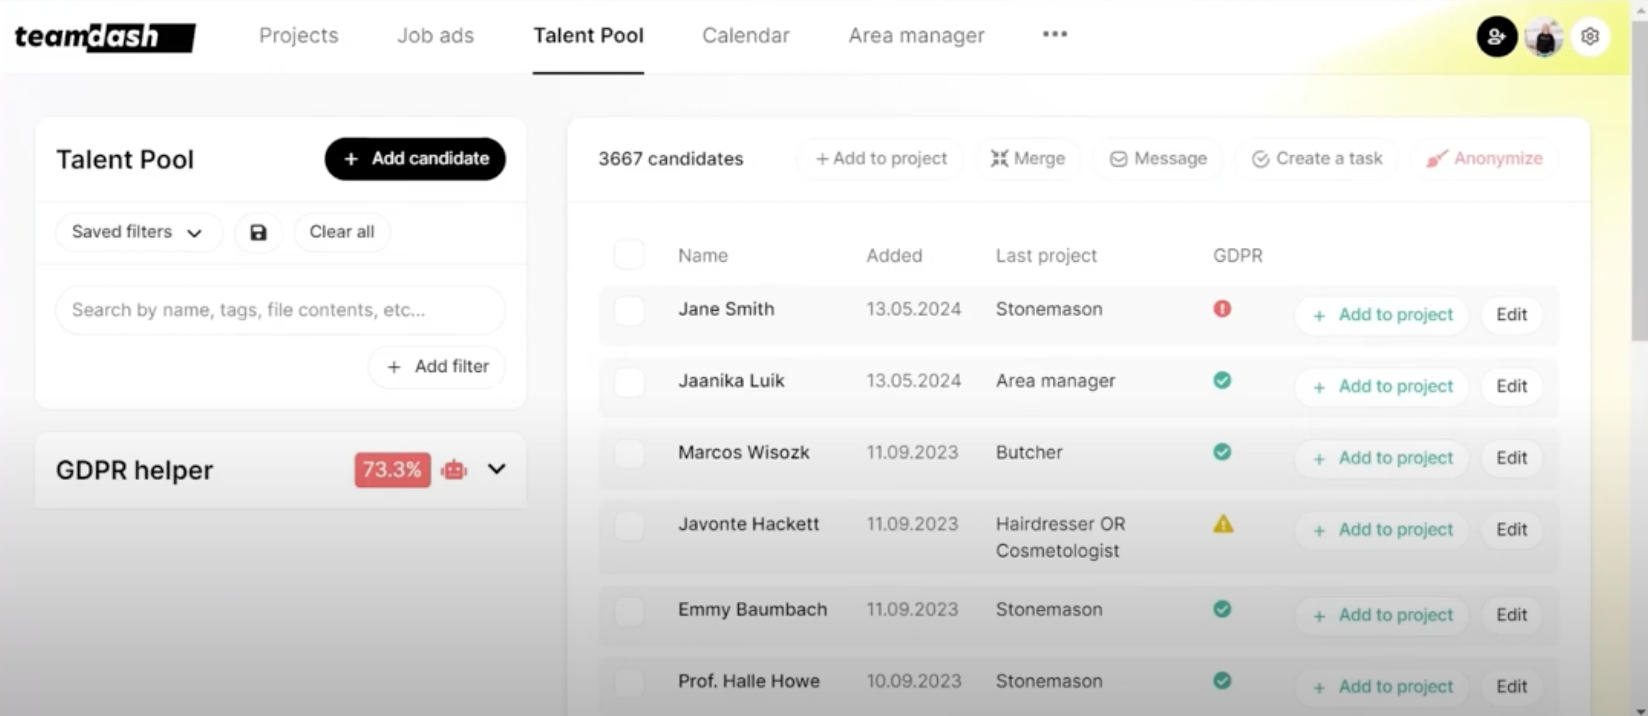
In Teamdash, head office keeps one set of rules while each team sets its own GDPR contact, privacy policy, dispute period and consent messages. See how GDPR compliant recruitment software works across teams and countries.
What can you do to ensure GDPR compliance in your company?
- You need to have internal data processing policies in place. Everybody in your company should know how to handle recruitment data that is trusted to them. It’s also important to provide regular training to raise awareness of data protection.
- Use secure and GDPR compliant recruitment software. This helps ensure data processing agreements are in place and candidate data is processed correctly and kept secure.
- You need to look at your talent database and verify whether some data needs to be deleted or updated, whether consents are updated, etc.
- You should be ready to address any data breach incidents. You might need to notify the local data protection authority and the data subjects themselves as well, so it would be good if you had protocols for doing so.
- You should be aware of the candidate’s rights regarding their data and be ready when they exercise those rights.
The risks of non-compliance with GDPR
A legal entity can also be held liable if it has been inactive and hasn’t complied with any of the obligations under the GDPR or if its actions have not been in compliance.
These breaches can result in financial penalties imposed by the government may amount to up to 20 million or up to 4% of the global turnover, whichever amount is higher. Data subjects can file complaints for data breaches. You can end up being in legal disputes – if somebody can prove that you’re not respecting the rights to privacy and have damaged them, you can also be responsible financially.
Another risk of non-compliance is reputational damage. This damage can be on a wider scale – on social media or press. You can attract audits and investigations from supervisory authorities, and in some countries, you can face criminal charges in such cases. It could lead to being excluded from certain projects like public tenders whenever you have a known history of not being compliant with the data protection requirements.
GDPR checklist for recruiters
- Know which candidate data you collect, why, and on what legal basis.
- Collect only what you need to judge whether someone fits the role.
- Give candidates a clear privacy notice before they apply, in their language.
- Ask for separate, freely given consent for your talent pool and for contacting referees.
- Set retention periods, and delete or anonymise data when they end.
- Keep interview notes factual and job-related. Candidates can ask to see the data you hold about them, notes included.
- Share candidate data only with people who need it.
- Agree with recruitment agencies who is responsible for the candidate data they send you.
- Have a data processing agreement with every tool and provider that handles candidate data.
- Answer candidates’ requests about their data within one month.
- Have a plan for data breaches. Most breaches must be reported to the supervisory authority within 72 hours.
Keep candidate data GDPR compliant with Teamdash
Keeping a talent pool GDPR compliant takes ongoing work, and it gets harder when you hire across several teams and countries. Teamdash has the tools built in, so the rules you set are followed in every team.
- Track consent for every candidate, and send renewal requests automatically or in bulk.
- Anonymise candidates automatically when their consent runs out, with permanent deletion as an option.
- Let each team use its own GDPR contact, privacy policy, dispute period and renewal messages, in its own language.
- Give access by role and project, so hiring managers only see their own projects and confidential projects stay restricted.
- Rely on a platform that’s built and hosted in Europe, stores candidate data in the EU, is ISO 27001 certified and comes with a digitally executable DPA.
Explore GDPR compliant recruitment software
This article is based on our webinar “Ensure GDPR Compliance in Recruitment Like a Pro”, you can watch the recording on Youtube.

